CIO · CISO · Austin, Texas
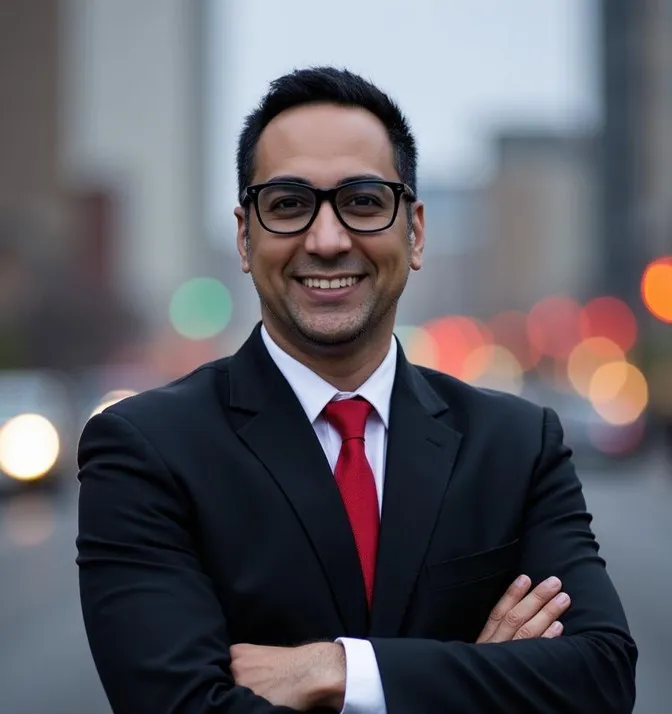
Masoud Heydari
I run IT, cybersecurity, and AI as one program, at the CIO and CISO level. In 20 years I’ve gone from building networks to briefing boards, and I still work both ends.
The companies I lead get one executive for the infrastructure, the security program, the CMMC or SOC 2 assessment, and the AI rollout.
- 20 years
- across IT, cybersecurity, and AI
- CIO · CISO
- Fractional executive roles since 2024
- CMMC
- plus NIST 800-171, SOC 2, HIPAA, PCI-DSS
- MBA · PMP
- and CompTIA SecurityX
About me
A decision about identity, data, or a new AI tool lands on IT, security, and compliance at the same time, so I hold all three together: one roadmap, one budget, one risk register.
My background covers the full stack. I’ve rebuilt data centers for PCI-DSS, moved companies to the cloud, built detection and incident response programs, and taken organizations through SOC 2, HIPAA, and NIST audits. I’ve led incident response at 2 a.m. and briefed the board on the same event a week later.
Defense contractors bring me CMMC work. I map their environment to NIST SP 800-171, close the gaps, and build the evidence package an assessor will ask to see.
AI sits inside the same program. I help leadership choose which tools to adopt, set what data those tools can reach, and give the security team a way to monitor them.
I studied computer science at Troy University, earned an MBA at Georgia Southwestern State University, and live in Austin, Texas.
The path so far
From network closets to the executive briefing room.
- 2024 – now
Fractional CIO and CISO
I serve as the senior IT and security executive for mid-market companies. I own the technology roadmap, the security program, CMMC and SOC 2 readiness, AI governance, and vendor management, and I act as incident commander when a serious event hits.
- 2023 – 2024
Head of IT and security, 150-person firm
I owned IT and security for a 150-person venture firm. I built the new headquarters on zero-trust controls, wrote the core security policies, and moved operations from an outside provider to an in-house team.
- 2022 – 2023
Security and compliance consulting
I led SaaS, security, and compliance projects for more than 20 clients and took several from unprepared to SOC 2 audit-ready in about four months.
- 2018 – 2021
Systems engineering in hospitality
I rebuilt on-premises data centers to meet PCI-DSS, segmented payment networks, and migrated property systems for hotels while holding 99.9% uptime.
- Early career
IT operations and network builds
University IT operations, then the network backbone for an automotive assembly line.
Credentials
Education, certifications, and training.
- MBA
- Georgia Southwestern State University, 2025
- B.S. Computer Science
- Troy University, minor in mathematics
- Beta Gamma Sigma
- Honor society for business schools, inducted 2025
Active certifications
- PMP, Project Management ProfessionalProject Management Institute · since 2024Through 2027
- CompTIA SecurityX ce (formerly CASP+)CompTIA · since 2024Through 2027
Additional certifications
- Six Sigma Red Belt Georgia Southwestern · 2025
- CompTIA A+ CompTIA · 2013
- MCSE, Microsoft Certified Systems Engineer Microsoft
- MCP, Microsoft Certified Professional Microsoft
- CCNA, Cisco Certified Network Associate Cisco
Platform certifications
- Datto Cybersecurity Kaseya
- Certified Tech, Datto Backup for Azure Kaseya
- Certified Tech, Datto SaaS Protection Kaseya
- IT Glue Certified Professional Kaseya
Continuing education
- Enterprise and IT architecture, cloud architecture, AI and machine learning, ethical hacking, technical product management LinkedIn Learning
- Cybersecurity Essentials, Introduction to Cybersecurity, Introduction to IoT Cisco
- Internet History, Technology, and Security University of Michigan
How I lead
Four rules I bring to every IT and security program I run.
One owner for IT, security, and AI.
Access, data, and vendor decisions touch all three. I run them on one roadmap with one risk register, so no control sits between two teams with nobody responsible for it.
Show me it works.
A policy says what should happen. A log, a test result, or a screenshot shows what did happen. I ask for the second kind before I sign off.
Compliance comes from operations.
If your controls work and your team collects evidence as it goes, a CMMC or SOC 2 assessment reviews what you already do. I build programs that way from the first month.
Brief each person in their own terms.
A board member needs the dollar exposure and the deadline. An engineer needs the CVE and the patch. I write both versions of the same risk.
Quick answers
- Who is Masoud Heydari?
- Masoud Heydari is a CIO and CISO-level technology executive based in Austin, Texas. He leads IT, cybersecurity, and AI as a single program, with 20 years of experience across infrastructure, security operations, cloud, and compliance.
- What does Masoud Heydari do as a fractional CIO and CISO?
- He serves as a company’s senior IT and security executive without a full-time hire. The role covers the technology roadmap, the security program, compliance, AI governance, vendor management, and incident command.
- Does Masoud Heydari work on CMMC?
- Yes. He helps defense contractors prepare for CMMC by mapping their environment to NIST SP 800-171, closing control gaps, and building the evidence an assessor reviews. He also leads SOC 2, HIPAA, and PCI-DSS readiness.
- How does he approach AI?
- He treats AI as part of the IT and security program. He helps leadership choose AI tools, limits the data those tools can reach, and sets up monitoring so the security team can see how they are used.
- What is Masoud Heydari’s education?
- He holds an MBA from Georgia Southwestern State University (2025), where he was inducted into the Beta Gamma Sigma business honor society, and a B.S. in Computer Science with a minor in mathematics from Troy University. His PMP and CompTIA SecurityX (formerly CASP+) certifications are active through 2027. He also holds Six Sigma Red Belt, CompTIA A+, MCSE, MCP, and CCNA certifications.
- How can I contact Masoud Heydari?
- LinkedIn is the best way to reach him: linkedin.com/in/masoudheydari.